

My Friday SIEM post is here, this week the two SIEM onboarding religions.
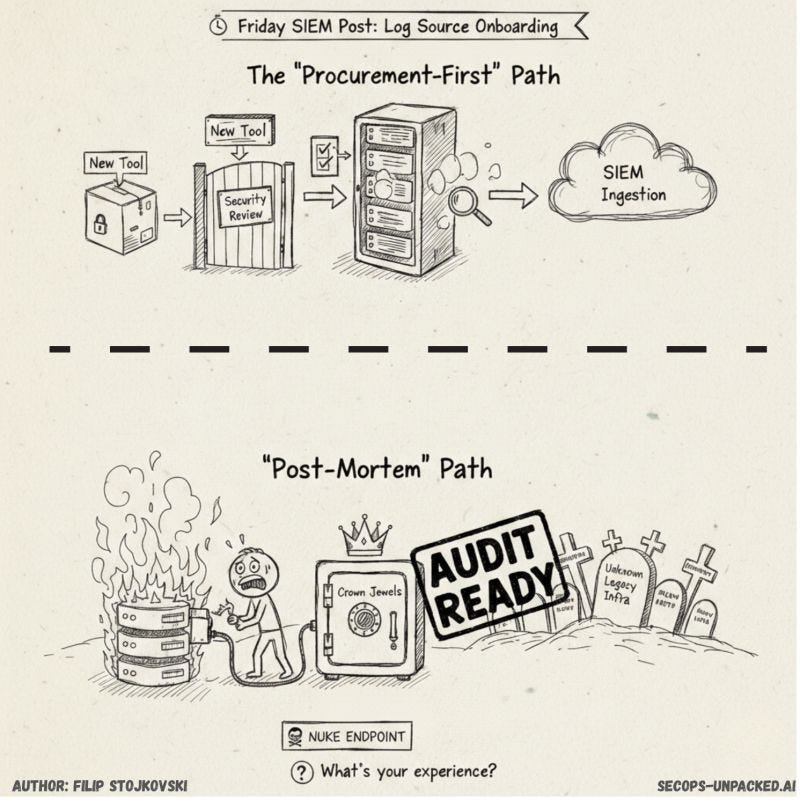
From what I have experienced so far :
Onboard by design
New tool comes in → security review → confirm log capability → ingest + normalize → monitoring is part of initial setup.
✅ Rarely hear “we don’t have logs”
✅ Better investigations, better accountability
❌ Costs show up immediately (ingest + retention + engineering)
❌ Eventually you hit a human bottleneck: triage/IR bandwidth
Onboard by pain
List crown jewels + auditor baseline → everything else is backlog until an incident happens → post-mortem drives new onboarding.
✅ Lower steady-state cost
✅ Smaller monitoring surface area
❌ Investigations stall: “can’t go further, no telemetry”
❌ Response becomes “nuke endpoints / reimage dev servers” because evidence is missing, pray you don't hit production
❌ Post-incident onboarding queue becomes permanent debt
Neither is “right” without saying what you optimize for: risk reduction, audit coverage, or cost control.
Is this what you see as well , and what’s the one question you usually ask before onboarding a log source?
Originally posted on LinkedIn on 6 February 2026.
Read the original post and the comments.