

My Friday SIEM post is here > AI Copilots in SecOps are splitting into 2 camps, and both are right (depending on your mess).
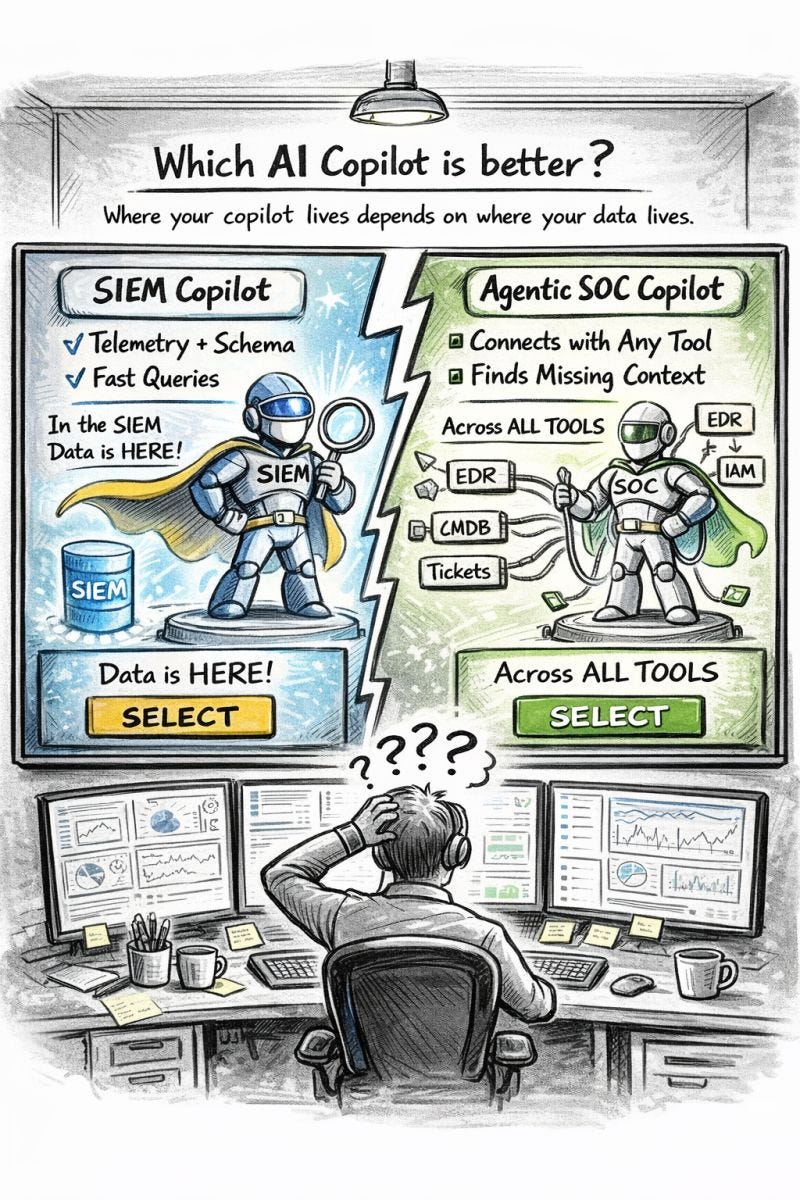
1) SIEM Copilot is amazing when you keep (almost) everything in the SIEM
Not just alerts.
Telemetry + good schema = you can hunt without the headache of writing custom queries. Start by checking available data sources and schemas, then pivot and grab what you need. Some argue copilots aren't optimized. My question: are we as humans?
In every org I've worked, someone eventually runs index=*. With the right query timeouts and read-only permissions, copilots work just fine.
2) If you don't send everything to the SIEM, move the Copilot up the stack
That's where Agentic SOC platforms make sense.
They connect to any tool, which means their copilots can reach into EDR, IAM, Cloud, CMDB, ticketing and pull the context your SIEM is missing.
3) Agentic SOC is harder than it sounds
It's not "connect API and done." You need to connect to all sources.
You need agents trained to interact with each one.
Many tools don't have APIs to run queries directly.
Others require 3-4 calls because the real details only come when you use their unique asset IDs. Then you work around rate limits, normalize fields, store it, and process it into something a human can actually use.
And if you thought MCP will fix this: I don't think so. Maybe it makes things easier if you use some AI chat desktop versions, but it's not the silver bullet. We wrote a full blog on this one.
The vendors that nail this will have a serious advantage. The tech exists. The solutions are cooking.
Where do you use AI Copilots today, have you tried both versions?
Do you query your SIEM from Claude?
Originally posted on LinkedIn on 30 January 2026.
Read the original post and the comments.