
This week I wanted to share some great reading materials and my take on federated search.
Anton Chuvakin dropped some really good SIEM posts this month, so this week is part reading list, part me weighing in.
🔸 The SIEM Zombie Apocalypse. Every “SIEM killer” wins a narrow argument, then runs into the rest of the job and ends up rebuilding a SIEM. You cannot fire the SIEM job.
This is just amazing article simply put how to save 100K of consultancy bill on SIEM architecture evaluation and migration plan.
https://medium.com/anton-on-security/the-siem-zombie-apocalypse-why-every-siem-killer-becomes-the-corpse-ac34af9e82e5
▫️ “I Don’t Need a SIEM, I Have Ollama!” Dumping days of raw logs into a local model is batch log review, not detection. The LLM writes the parser, it never runs as the parser.
https://medium.com/anton-on-security/i-dont-need-a-siem-i-have-ollama-yes-you-do-fd29174c44b5
And from Steve Cooper
Why 100% ATT&CK coverage still misses attacks. He cites a MITRE CTID study where 144 Sigma rules mapped to 84 techniques, yet only 26 had meaningful coverage. Score on procedures, not greens.
https://medium.com/@BlueTeamSteve/if-i-have-100-att-ck-coverage-why-didnt-i-detect-that-a6fda2101bb5
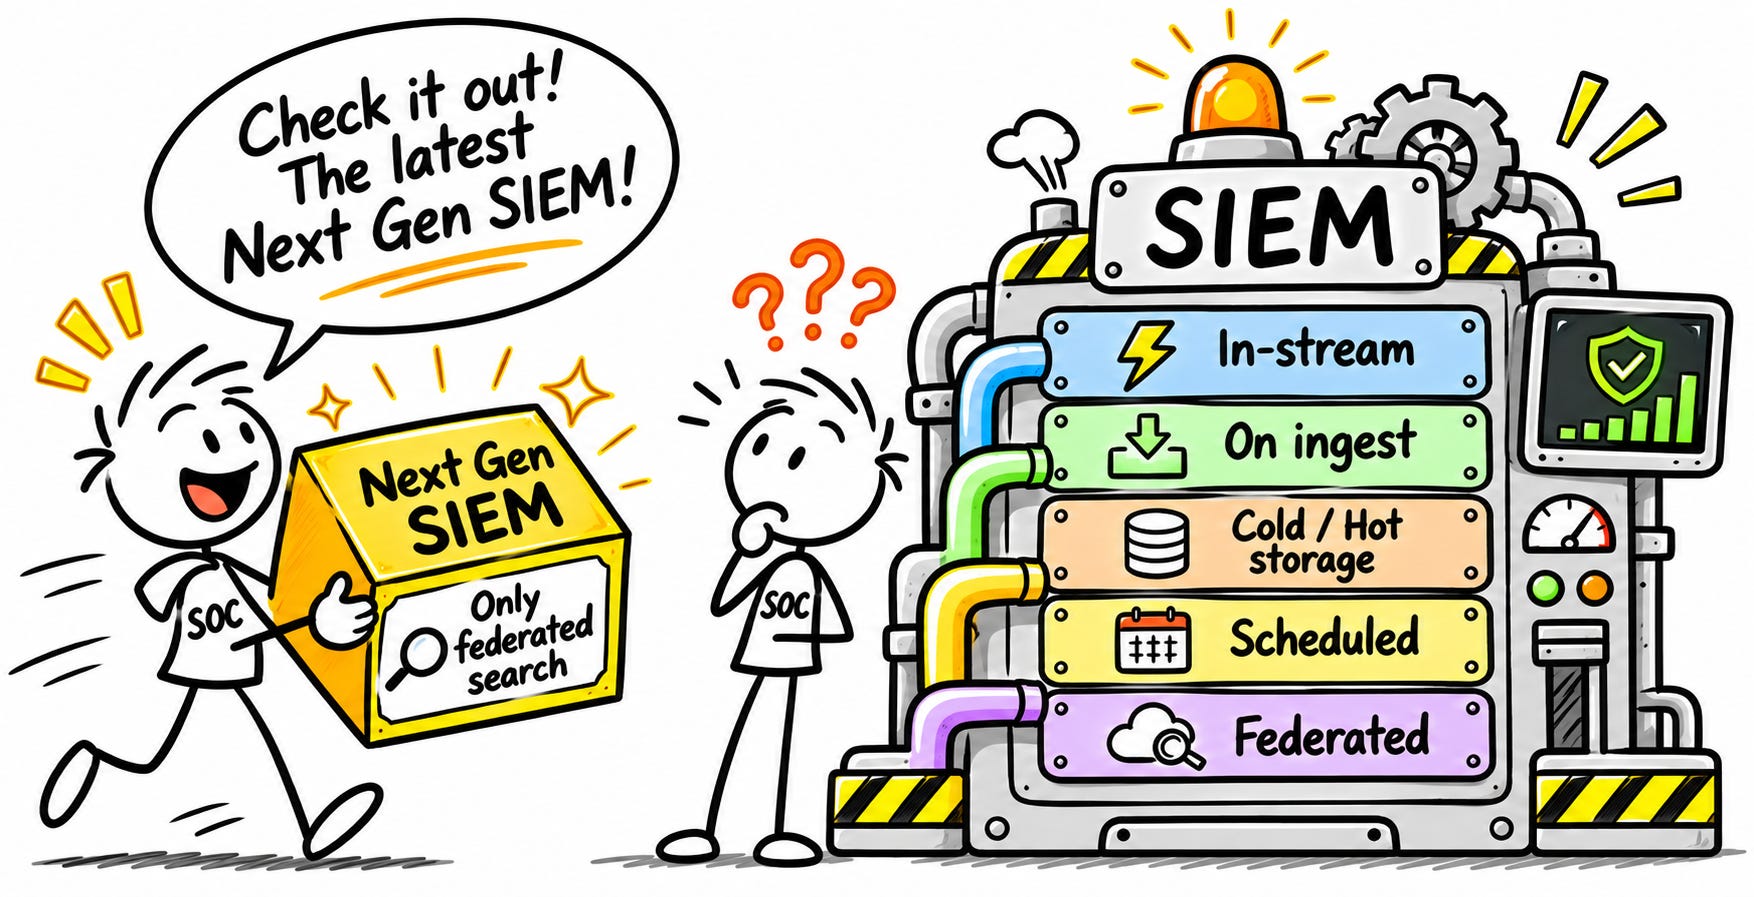
The thread across all three: claiming the capability is easy, doing the job is not. And the latest version of that I see is “federated SIEM” pitched as the way to replace your SIEM.
My read is that federated search is one SIEM capability, not a SIEM. It queries data at rest, in stores you don’t control, on demand or on a schedule. That is threat hunting and investigation, and it is very good at it. Real time happens in transit or as data lands, and right now we all want machine speed detections.
“But most SIEM rules are scheduled anyway.” True, and that is the better argument against federated detection. Every run over remote stores carries query cost, normalization at query time, source latency and someone else’s uptime.
So the word I have a problem with is “replace”. Federated search makes the SIEM you already have better: less ingest, longer reach, faster investigations. An upgrade to the stack, not a replacement of it.
And if we are serious about machine speed, I think detection is a lost game in many cases. Because even if you detect at machine speed you don't trust your automation to autonomously apply preventive measure.
What you need is machine speed prevention as well.
Have a siemless weekend ahead!
Read the original post and the comments on Linkedin
Discussion about this post