

From what I hear from many practitioners, we are going through the great SIEM migration. I think the last time this happened was when Splunk became a thing and everyone was moving to Splunk.
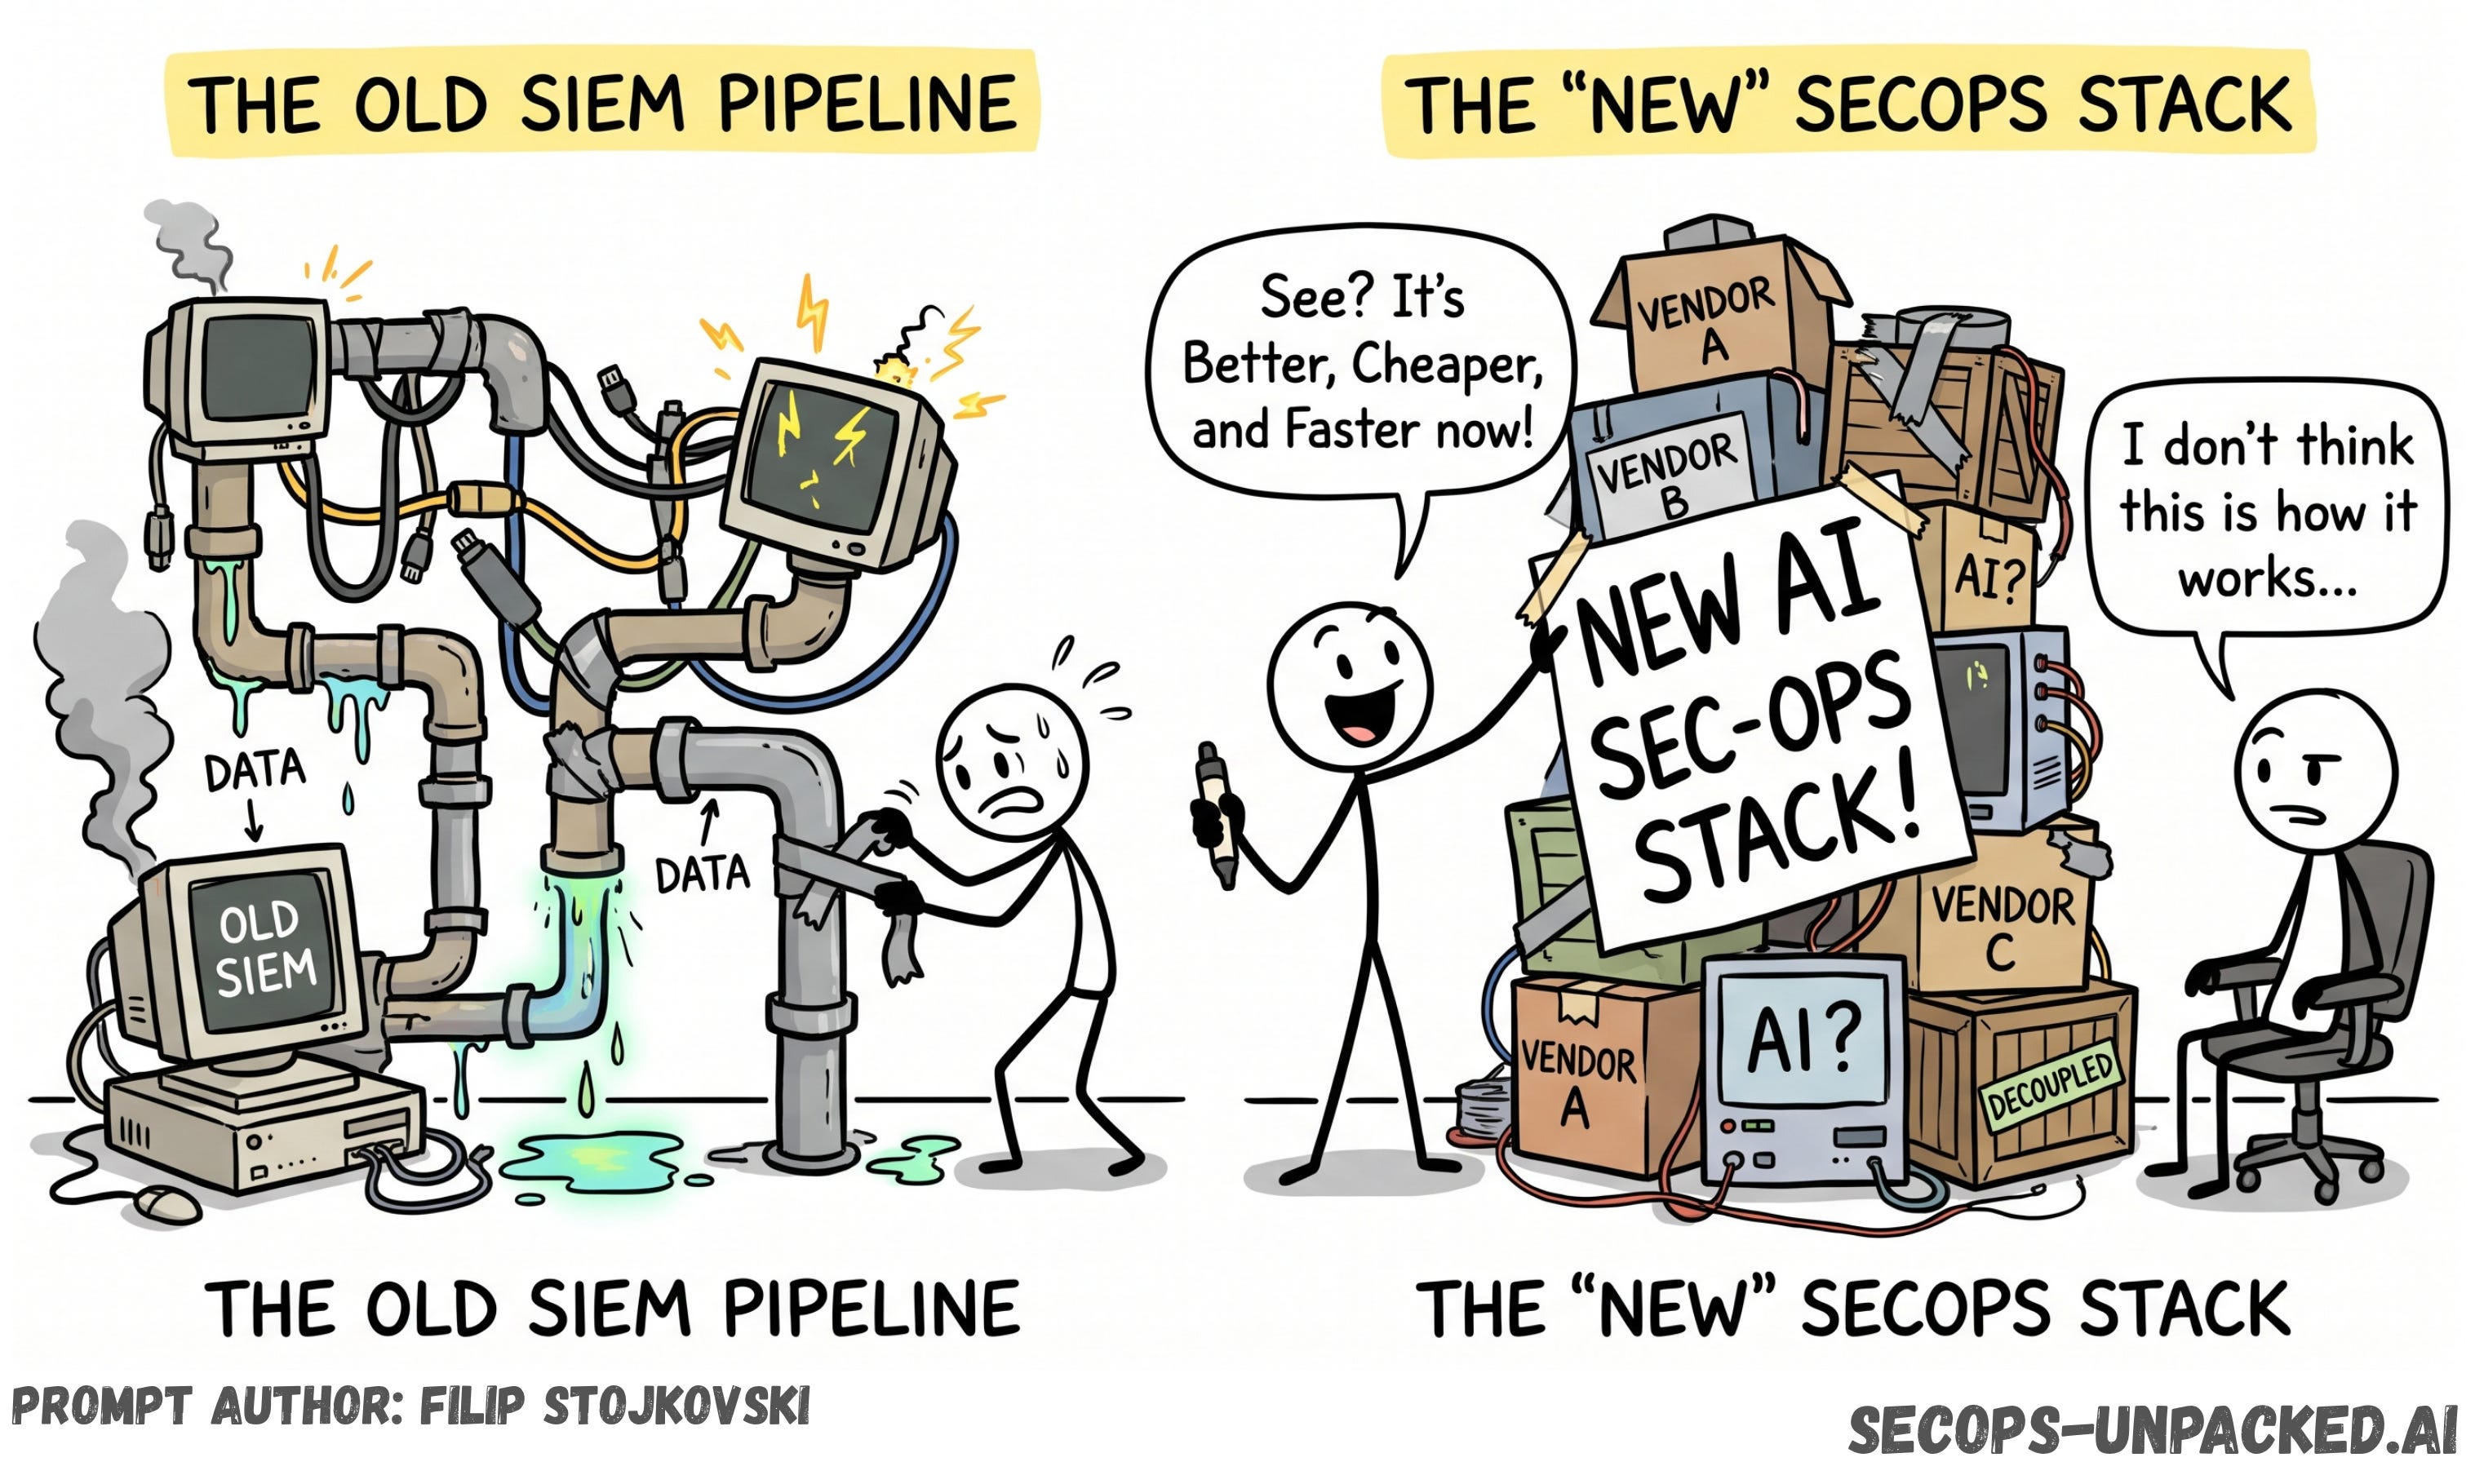
And it is not always about moving off the large vendors. Many teams are rethinking how they implement SIEM in the first place.
Because we now have so many tools that break down SIEM functionality, the evaluation is around what makes sense as a modern architecture. What stays in one platform, and what gets decoupled.
And yes, I think AI triggered this. Or I would say the evaluations for AI SOC started it.
Many teams started evaluating AI SOC to see how they can automate their SecOps faster and simpler. Then many came to the same realisation: you can’t just add AI and expect it to work. You need to change the way you work.
And once you change the way you work, you end up re-evaluating your whole security stack. SIEM included.
We see it on the vendor side too, as they build what practitioners ask for. SIEM vendors are rushing to add decoupled options, be more flexible, and ship AI SOC capabilities and agent builders. AI SOC vendors are moving toward becoming SIEM.
The two sides are meeting in the middle, and the SIEM label alone tells you less and less about what you are buying.
Migrate the SIEM before you change how you work, and you end up with the same SOC on a new platform.
Have a siemless weekend ahead!
Read the original post and the comments on Li
I think the strategic of bigger vendors is to include SIEM in their security platfrom. Some examples are Falcon of Crowdstrike, Xsiam Palo Alto and Microsoft with Unified portal ISOC. Moreover, agentic SOC like project perception of Microsoft.
I wonder what will be bugger security players in several years because AI security companies like OpenAI and Anthropic are investing a lot of money. What do you think?
Filip - "the same SOC on a new platform" is the line I'd hand every team running an AI SOC bake-off. Those evaluations keep turning into a data question: what can the agents actually see? (I'm at Stellar Cyber; our take: https://stellarcyber.ai/blog/the-siem-problem-is-an-architecture-problem/)