

I was doing some analysis this week on Context Graphs vs Knowledge Bases/Graphs, and I think we can easily get lost in all the “graph” terminology.
Many SIEMs now have some form of context, entity or security graph.
User → logged into → Host → connected to → IP
But there is another layer that matters as we move toward autonomous SecOps:
Why is this normal in YOUR environment?
Security is full of weirdness. If everything was perfectly locked down, nobody could get any work done. 😄 So companies make exceptions. Then exceptions on top of exceptions.
> A developer has root access to one production server.
> Two servers invoke PowerShell in a way that would normally make your detections scream.
Your SIEM can observe these , your context graph can connect them. But does it know why they exist?
As you know usually that knowledge sits in a ticket, a Slack thread, docs/confluence pages, or the head of the analyst who investigated the same thing three times and knows “yes, this looks insane, but it is expected.”
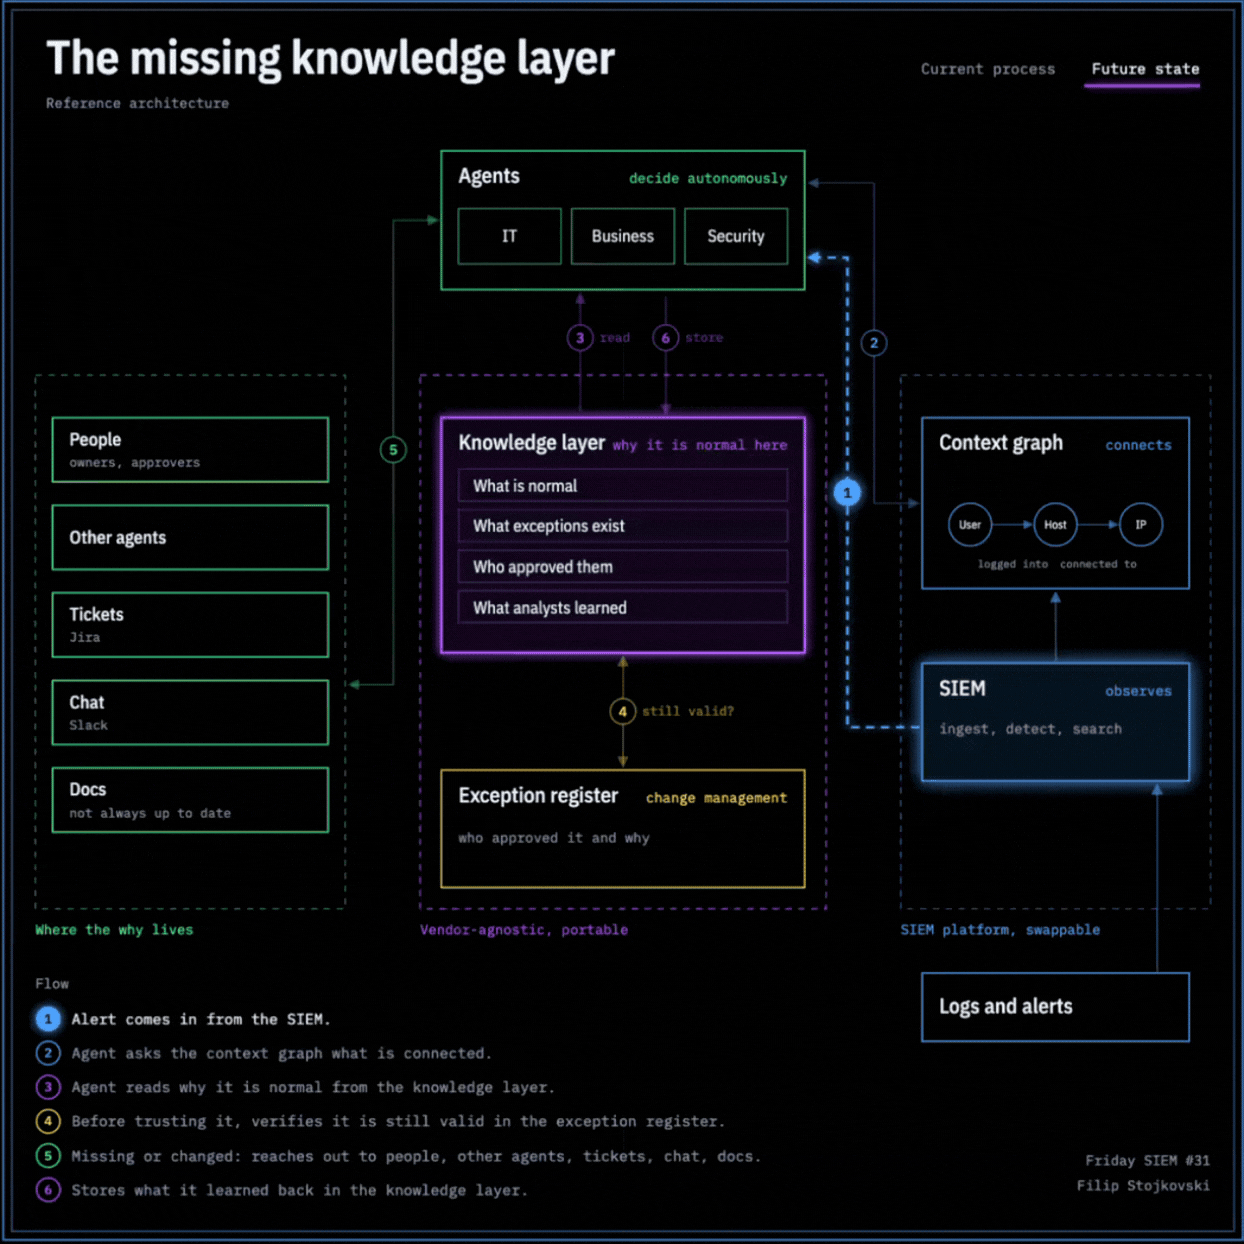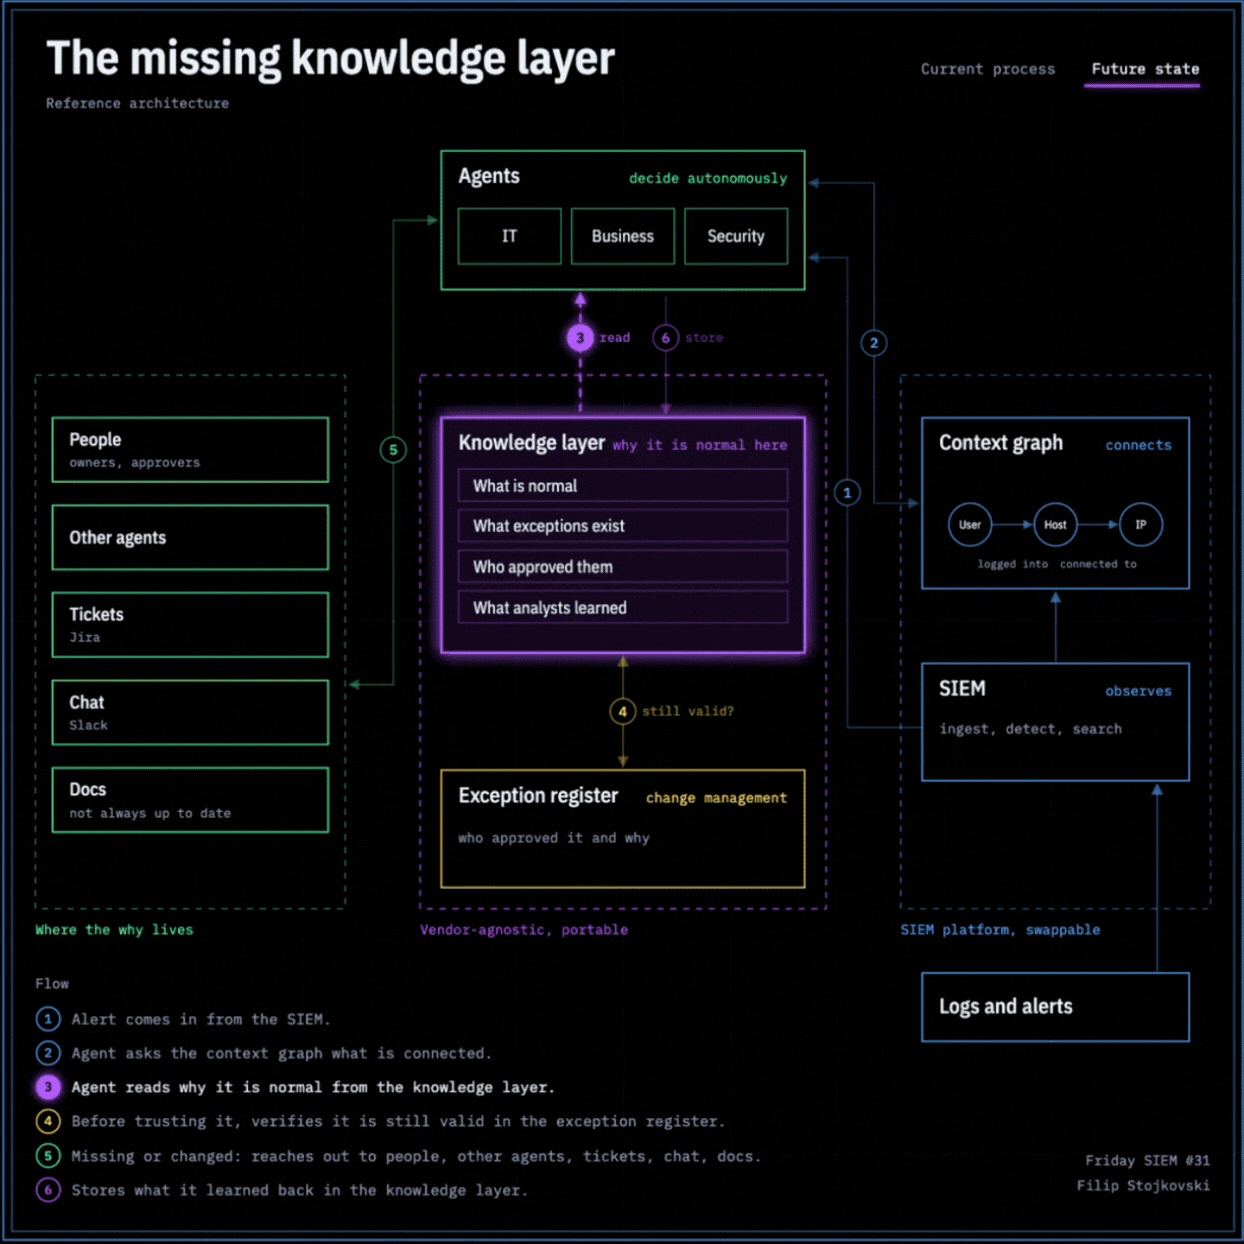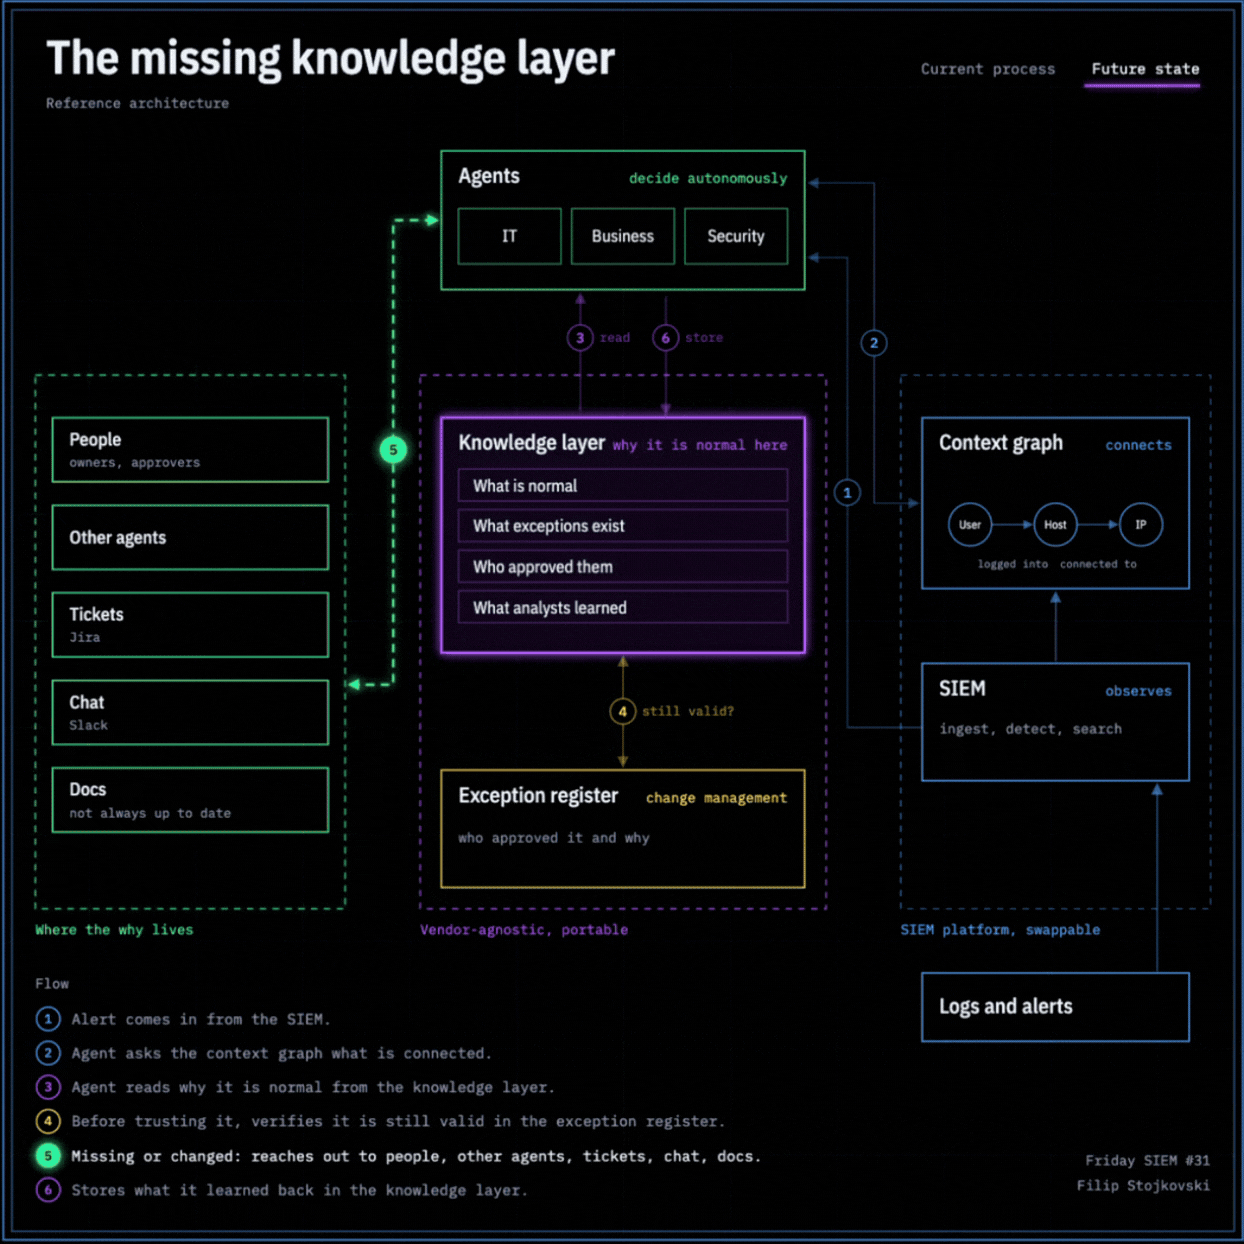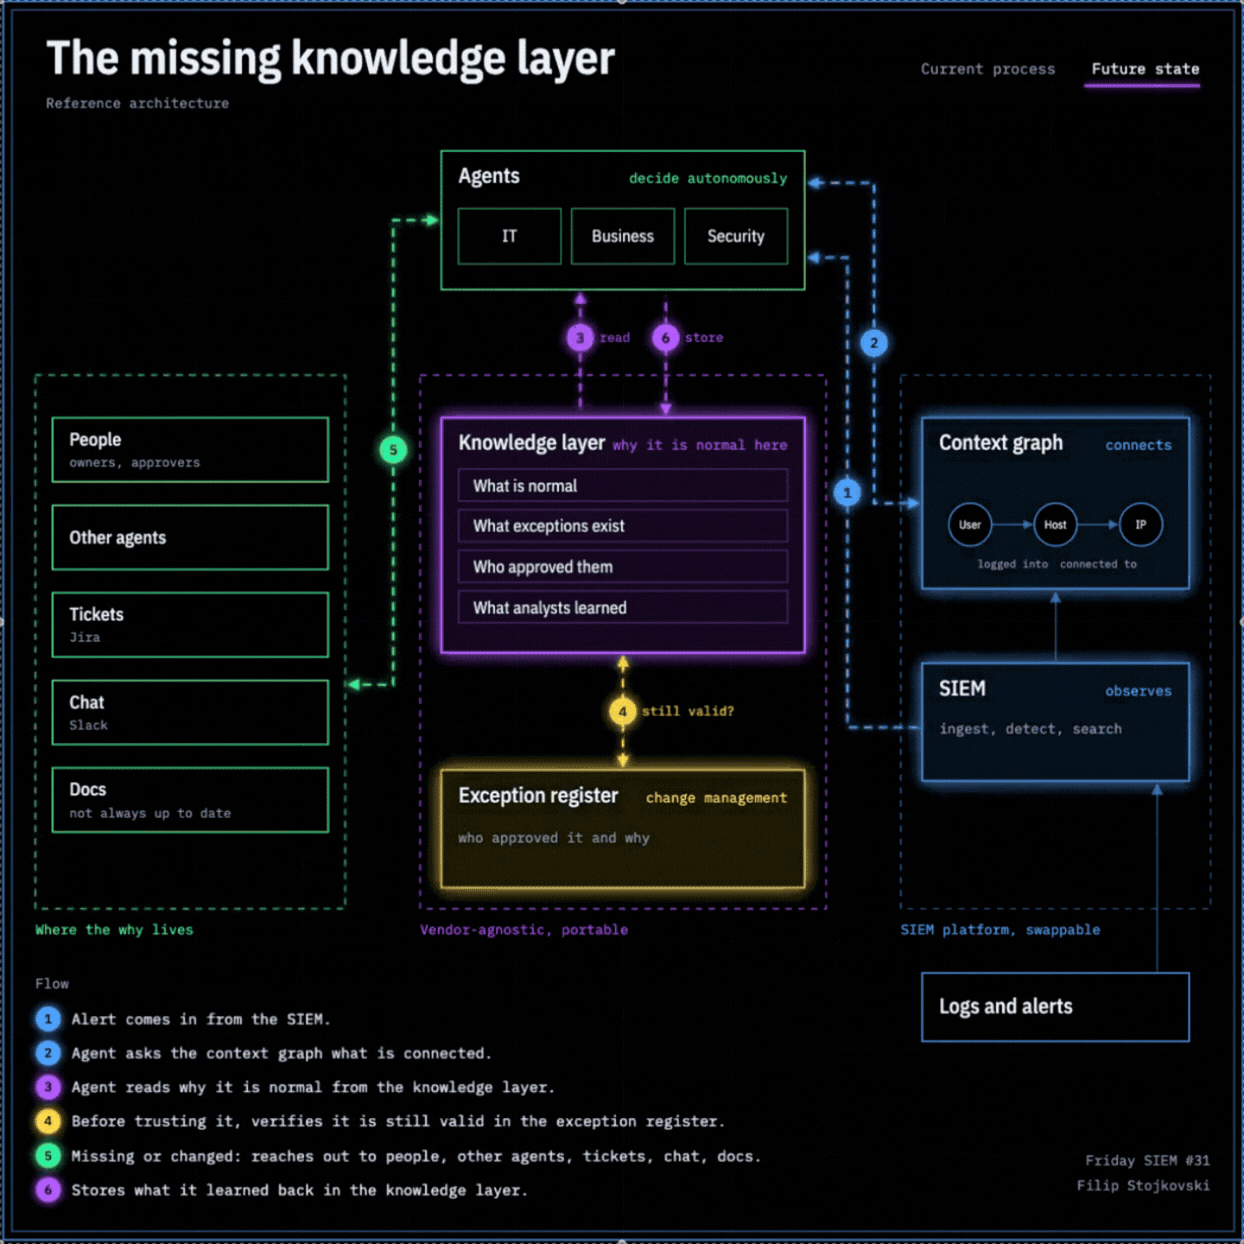
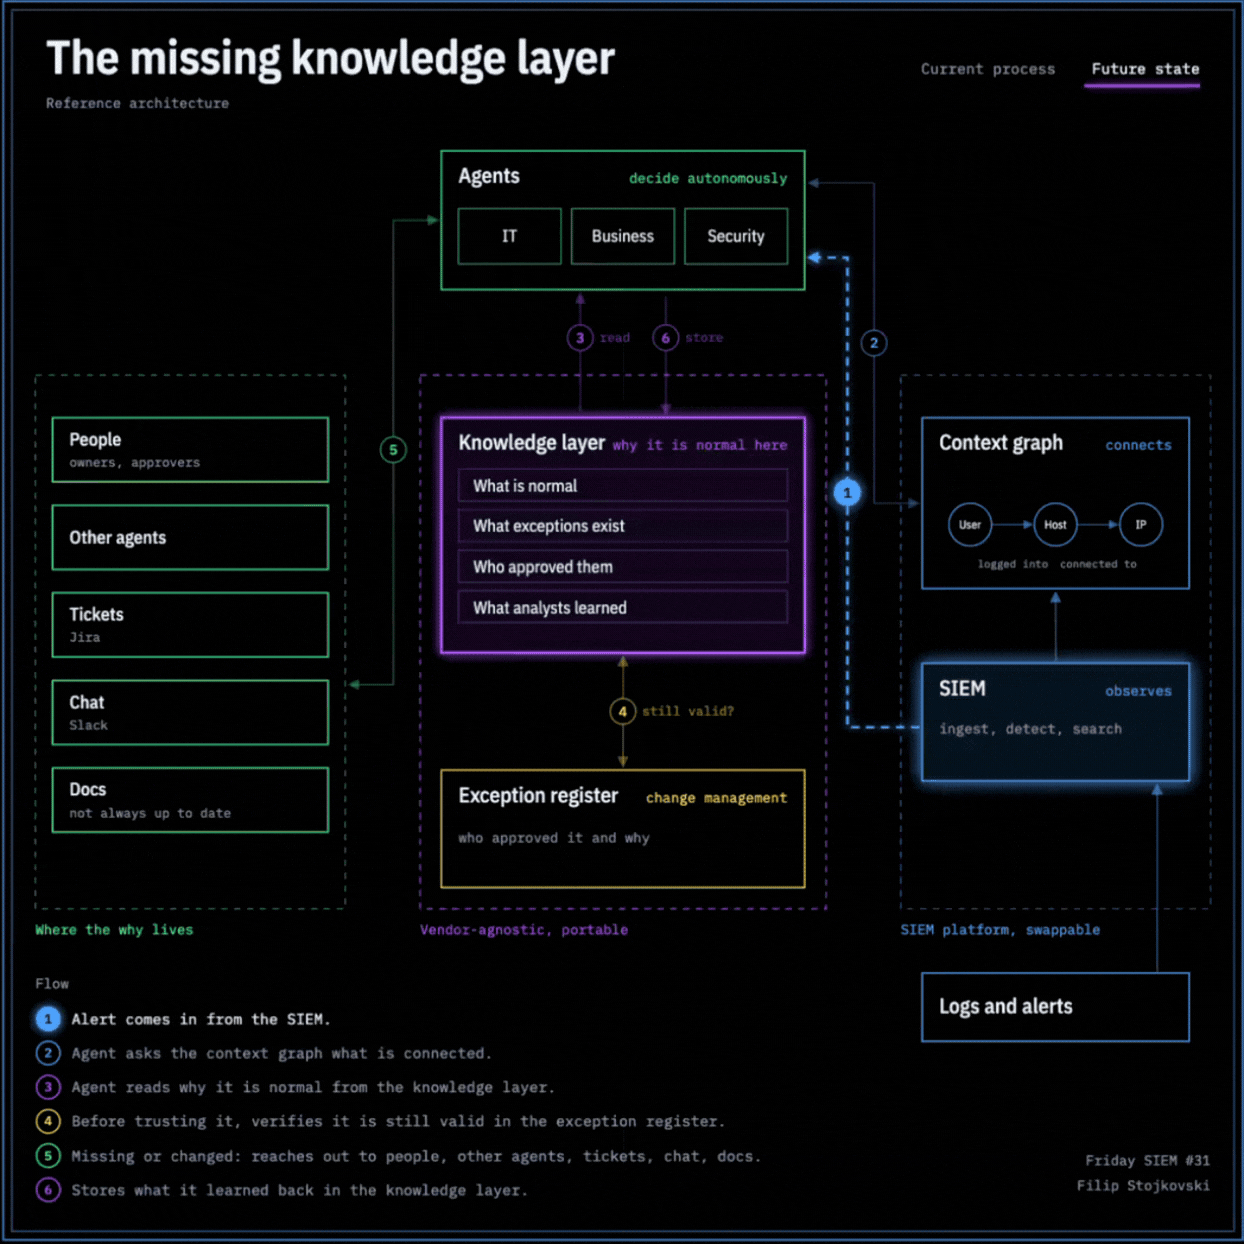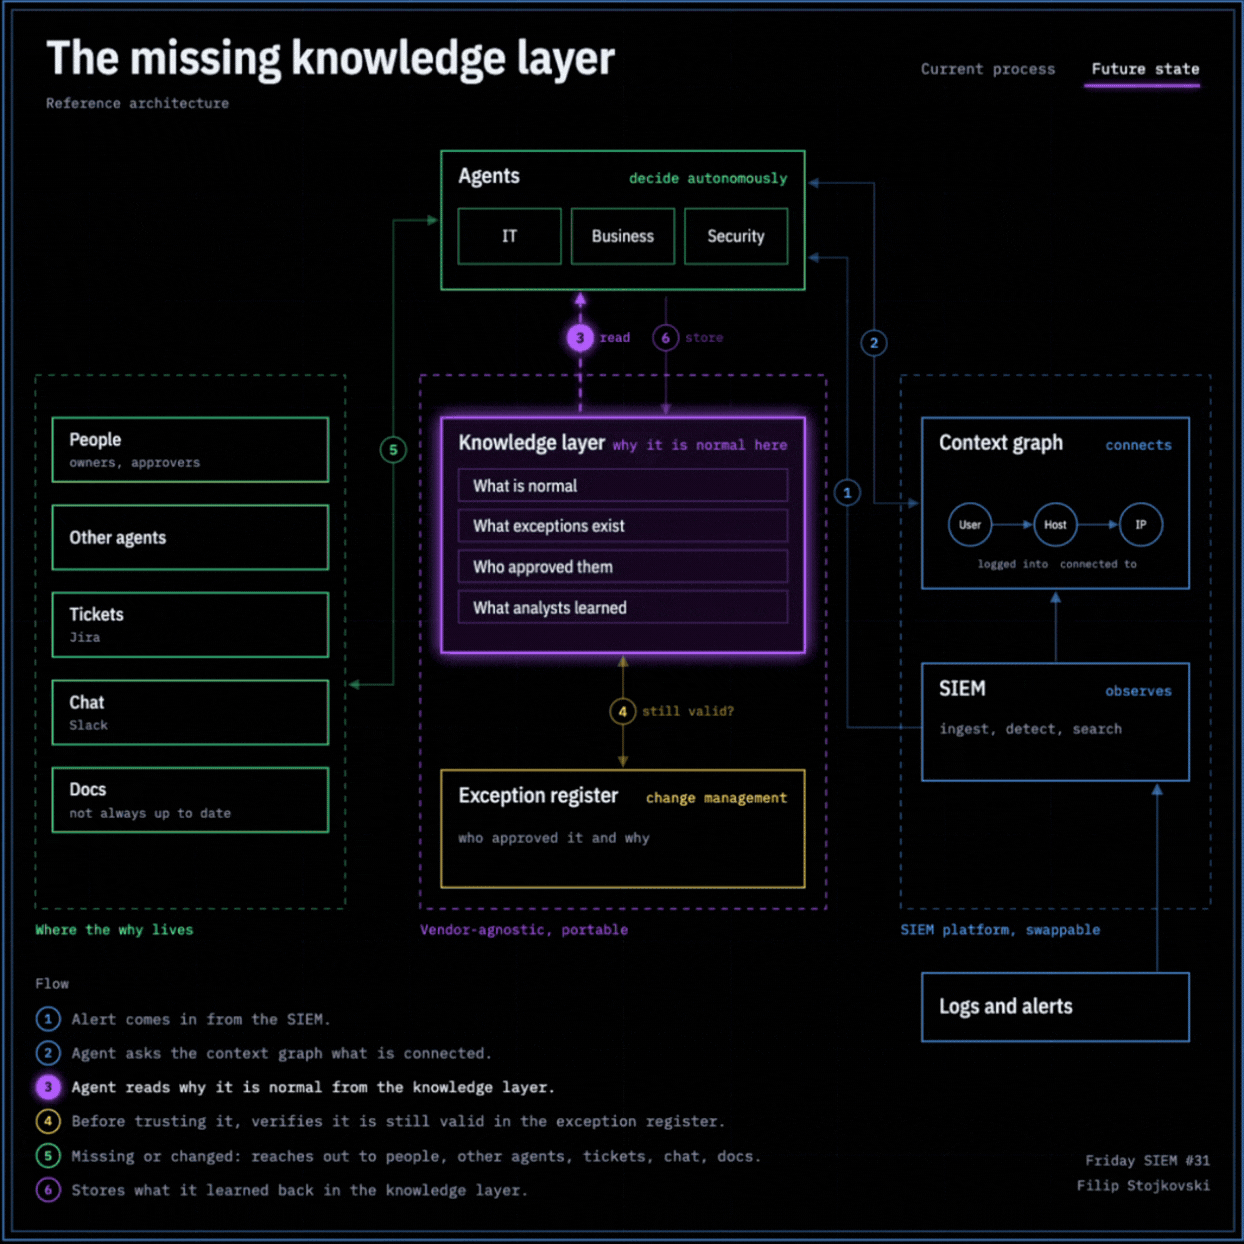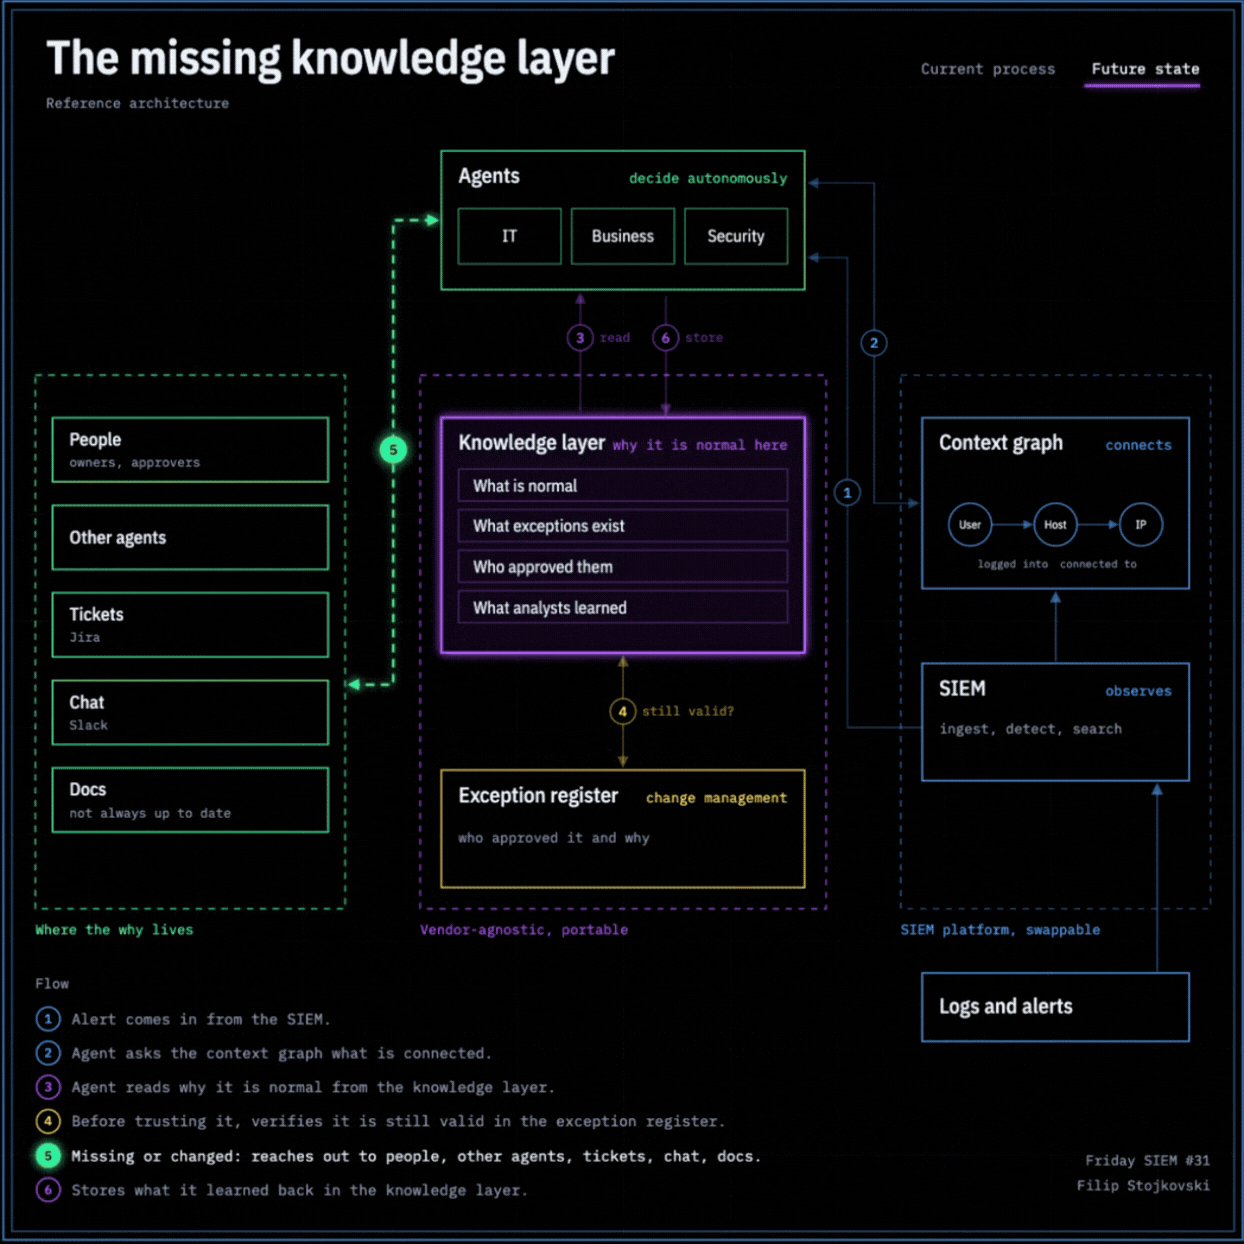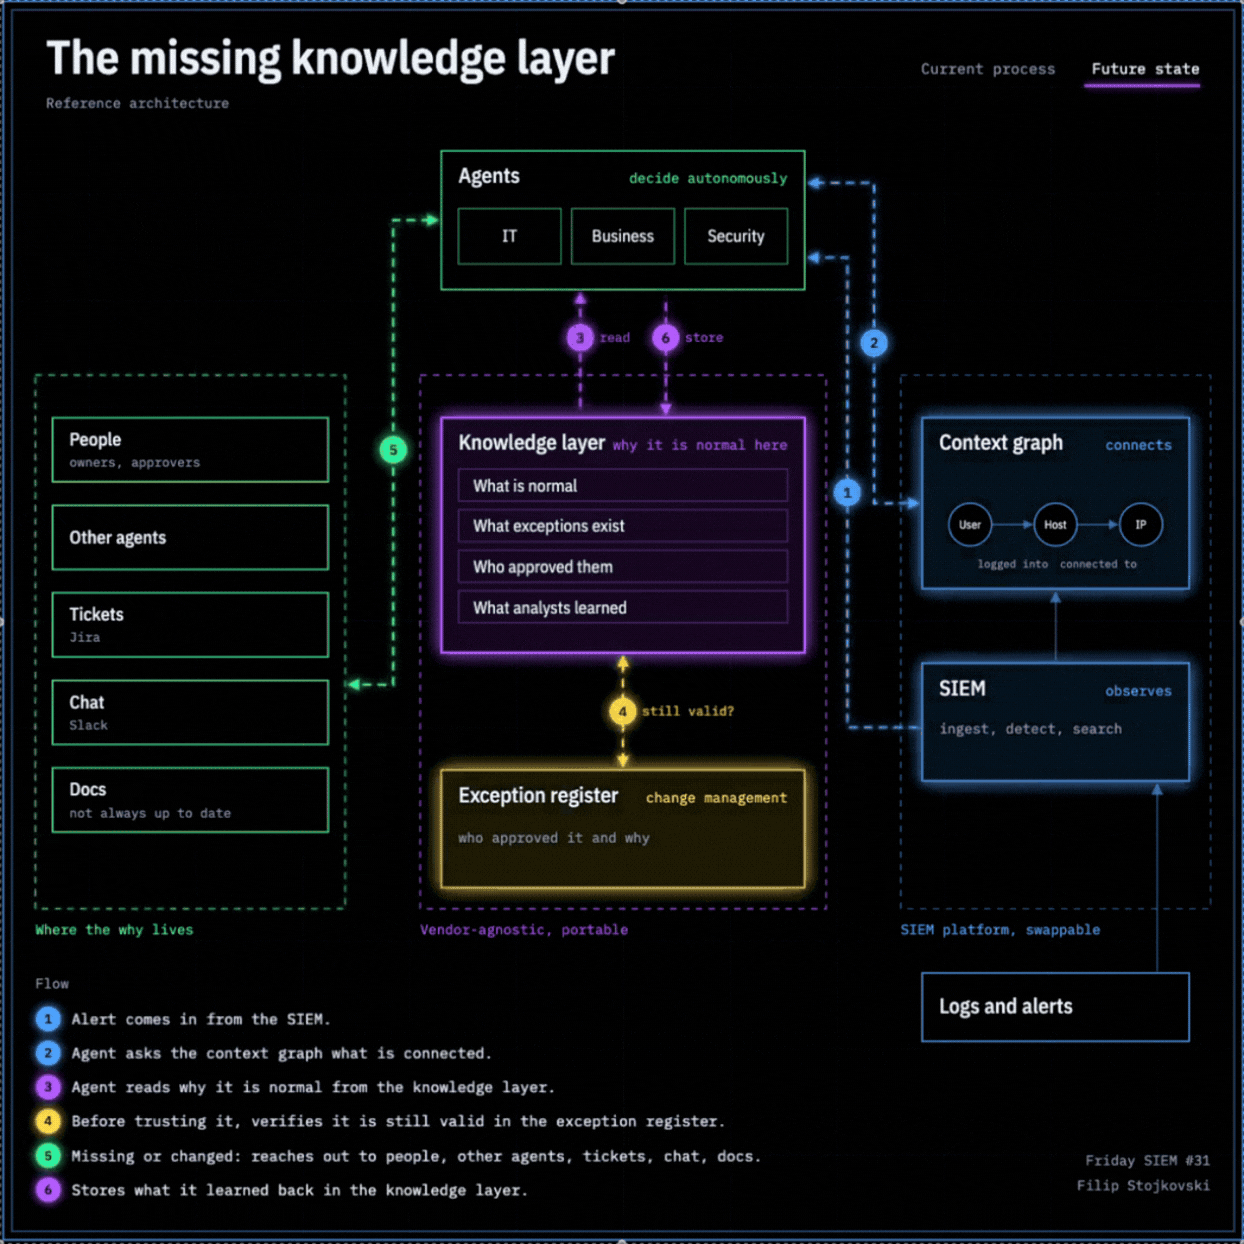
The knowledge layer.
Security knowledge about your tools and controls, combined with business knowledge/intelligence about how your organization actually gets work done.
If we want an agent to call it benign autonomously, more logs aren’t enough. It has to do the legwork the analyst does today: reach out to people or other agents, retrieve the why, and store it.
But this is tricky. It is not something you gather once and trust forever. Things change, so the agent has to verify nothing changed before relying on it. And if verifying means asking the same people again, they get pinged for the 10th time about the same thing.
The fix is a good way of tracking exceptions, change management, who approved it and why, recorded where the agent can check it.
Some AI SOC vendors are already building organizational knowledge/memory into their platforms, and some SIEM vendors are starting to. It is early, but I wouldn’t be surprised if SIEM vendors race to own it over the next 2-3 years, organically or through acquisitions.
Be careful where you build it. Context/Knowledge lock-in might become more painful than data lock-in. Logs are easy to move. Years of knowledge about
If this becomes one of your most valuable datasets, I would want it vendor-agnostic and portable.
Have a siemless weekend ahead!
Originally posted on LinkedIn on 25 September 2026
Read the original post and the comments
Check out our SecOps Market Landscape tracker and evaluation frameworks