

Friday SIEM post, and this week it is about the new SOC-CMM 2026 SOC maturity report
Great work as always by Rob van Os
There are few things caught my attention, and the first one is a SIEM story.
The SIEM is still the single pane of glass for most SOCs. 45% vs 24% for SOAR.
And I think I know why SOAR lost this battle.
🔸 Most SOAR platforms had way better case management than any SIEM. But it never connected well enough with the SIEM. In the end you had to jump back and forth to run queries and investigate, and if your investigation lives in one tool and your case lives in another, you consolidate on the one where you you have all the data to get the job done. That usually ends up being the SIEM in this case.
Funny enough, the same report shows SOAR has taken over as the primary automation tool (70% vs 45% for SIEM).
So SOAR won automation, lost the screen.
▫️Second, only 27% say they use AI embedded in existing tooling. Show me a security tool in 2026 that doesn't ship AI summaries by default. EDR, SIEM, email security, everything has an LLM baked in whether you asked for it or not. My read is not that the rest don't use AI, it's that they don't register it as using AI. When AI is a feature instead of a decision, it becomes invisible. Which also means every AI adoption number in every survey out there is probably understated.
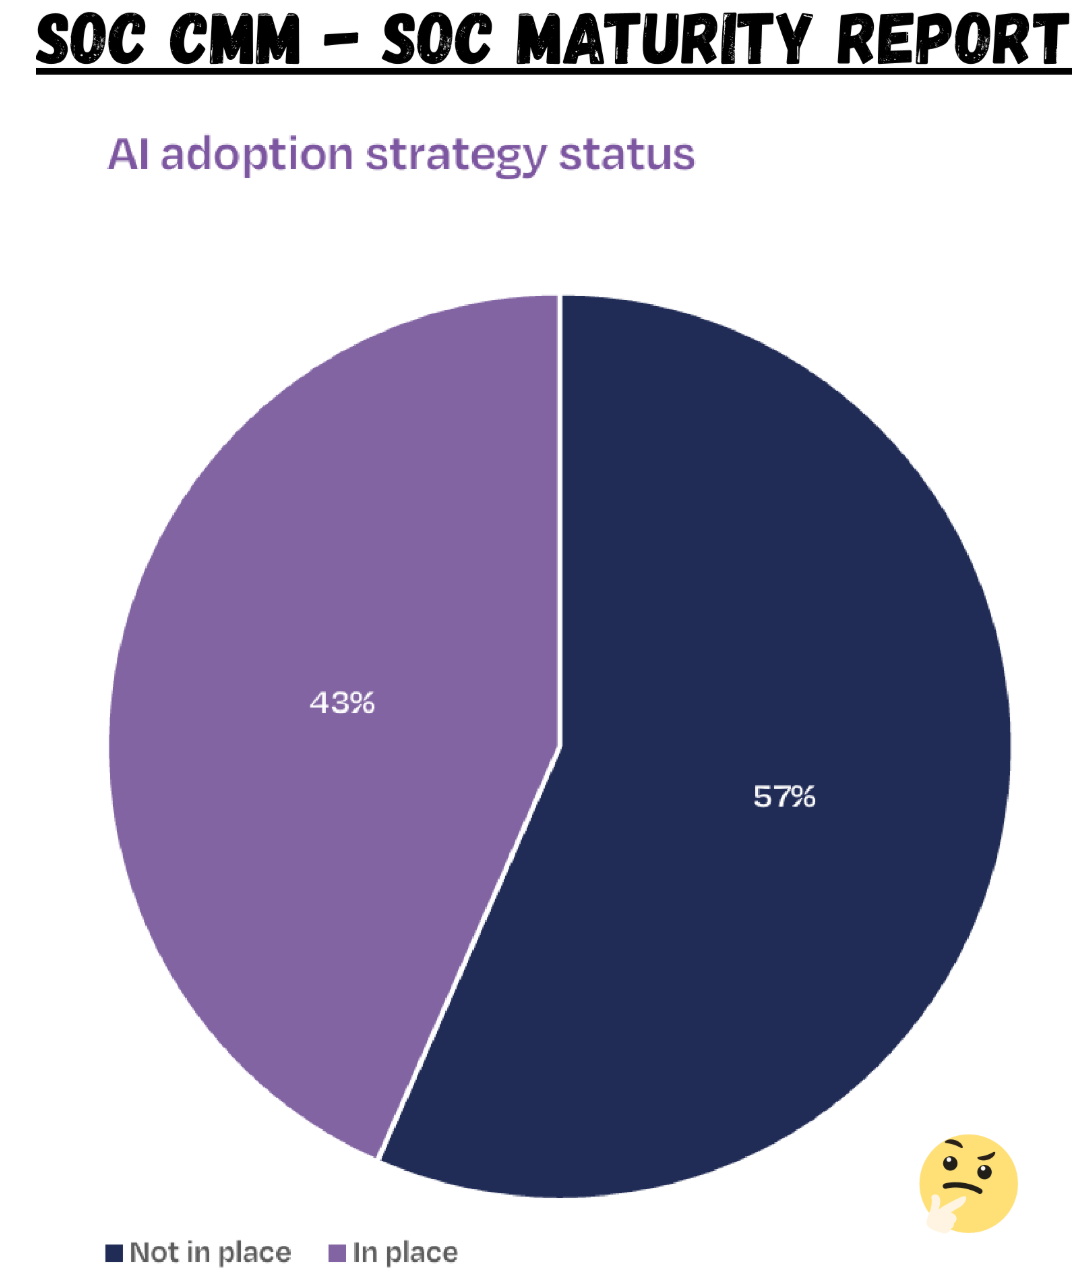
▫️ Third, the AI value numbers. Around 60% report seeing some value from AI in the SOC. But 57% also say they have no AI adoption strategy at all. So who answered the value question? If it's everyone, then people without a strategy (and possibly without real usage) are rating value, and of course you see no value in something you don't use. If it's only the AI users, then the value picture is a subset and shouldn't be read as "AI delivers limited value in the SOC". Before we conclude AI is underdelivering, I want to know the denominator.
Originally posted on LinkedIn on 28 August 2026
Read the original post and the comments