

Friday SIEM post, and this week it is about the flavors of SIEM. Or as it was put much better than I could: SIEM-not-SIEM.
Alex Hurtado put out a really good breakdown of the SIEM operating models this week . Traditional, Decoupled, Integrated SecOps, Federated, and Standalone.
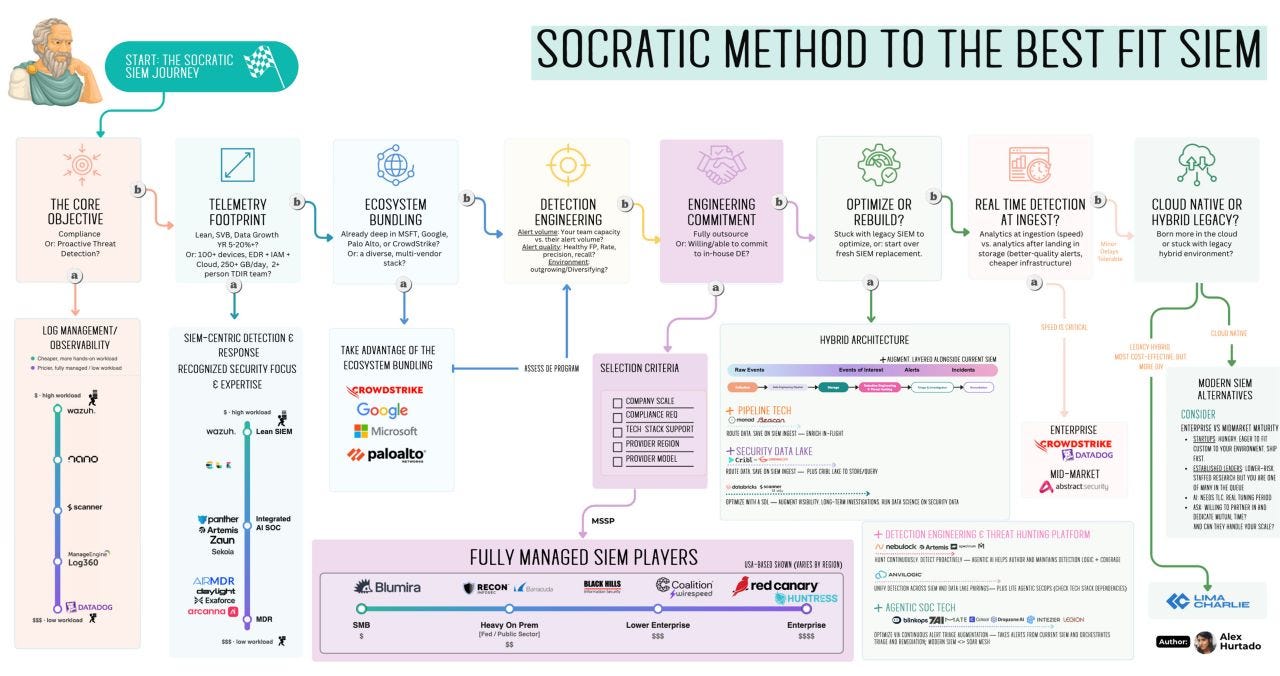
Love the visual, and yes, I think these are currently all the flavors and I see it as operating model map.
Every decision starts with questions about your environment. Your telemetry footprint. Your engineering capacity. Your ecosystem. Whether you’re rebuilding or optimizing. Whether you’re cloud native or still carrying legacy.
Choosing a SIEM it should depend on your PPT. Not the PowerPoint deck you’ll use to present your new SIEM, but your People, Processes, and Technology.
Changing the SIEM platform is only one piece.
Every one of these architectures assumes a different way of operating.
Different workflows. Different responsibilities. Different levels of engineering maturity. In many cases, a completely different skill set within the team.
Some models make perfect sense for lean teams that want simplicity and automation. Others only become practical when you have a larger team with dedicated engineering resources.
So now you have a great resource to help you with this 😀
Originally posted on LinkedIn on 14 August 2026.
Read the original post and the comments