

Friday SIEM post is here! This week: data pipelines to SIEM to AI SOC.
You probably saw the news, Cribl acquired CardinalOps (congrats to both teams).
The play makes a lot of sense.
Cribl has been moving toward the SIEM space for a while and the detection layer was the missing piece. CardinalOps gives them detection engineering, coverage assessment, finding broken and noisy rules. Not a full SIEM yet, but the direction is clear.
And they are not the only ones heading this route. We are seeing more and more players that started as data pipelines moving into SIEM and adding AI SOC on top. The AI SOC piece is what makes them compelling. In the past you needed SOAR-like capabilities to offer the investigation piece, now the agents cover that.
On the other side we see vendors that started as AI SOC moving left into the SIEM piece. Far left into data pipelines is harder to get. But that's where the demand is. Many orgs looking into AI SOC don't just want triage, they want to replace or consolidate their SIEM, MDR and SOAR costs. Every AI SOC conversation is a consolidation conversation.
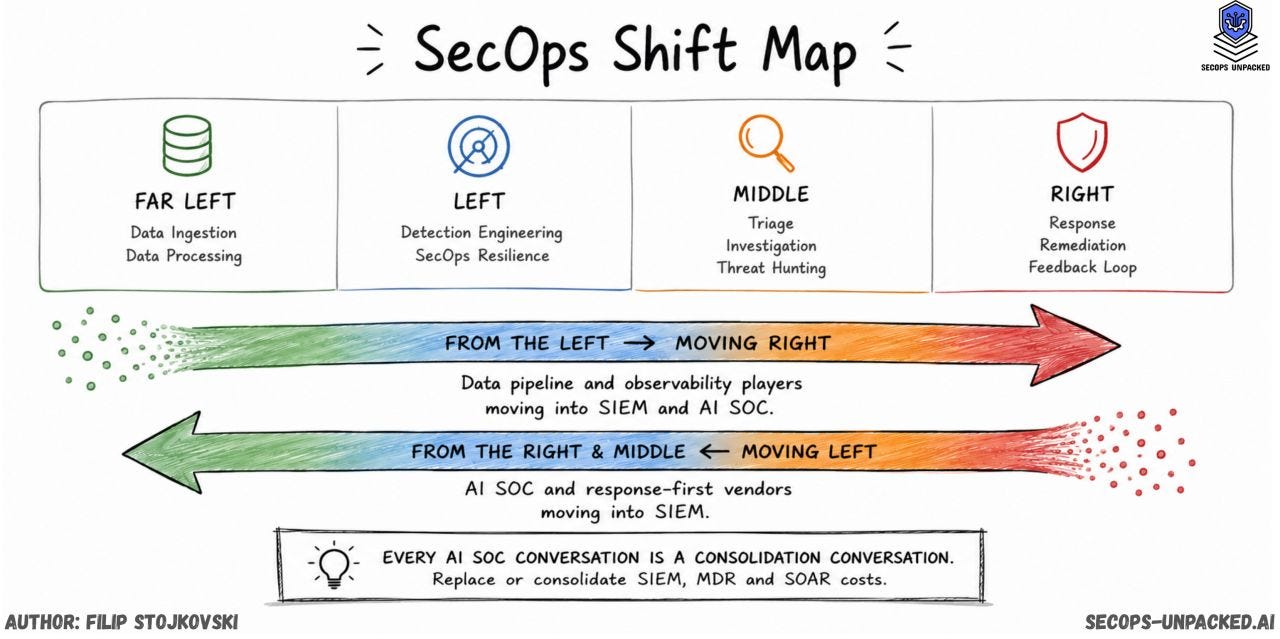
How I see this playing out, three types of implementations:
>> Platform play. This is where the ISOC category is getting stronger. The usual large players that offer everything.
>> Point solutions and decoupled SIEM. Many smaller solutions added to the stack, combo of vendors plus build it yourself.
>> Existing stack plus MDR and/or AI SOC on top. For those that want minimal tech disruption. And here I think the demand is high, AI SOC with MDR or MDR with AI SOC capabilities.
If you some additional play let me know, writing a full blog piece on this topic.
Originally posted on LinkedIn on 17 July 2026.
Read the original post and the comments.