

Friday SIEM: Almost every SIEM Has AI SOC
We currently track 32 vendors with both SIEM and AI SOC capabilities. But not all AI SOC pure play vendors has a SIEM (this is different category)
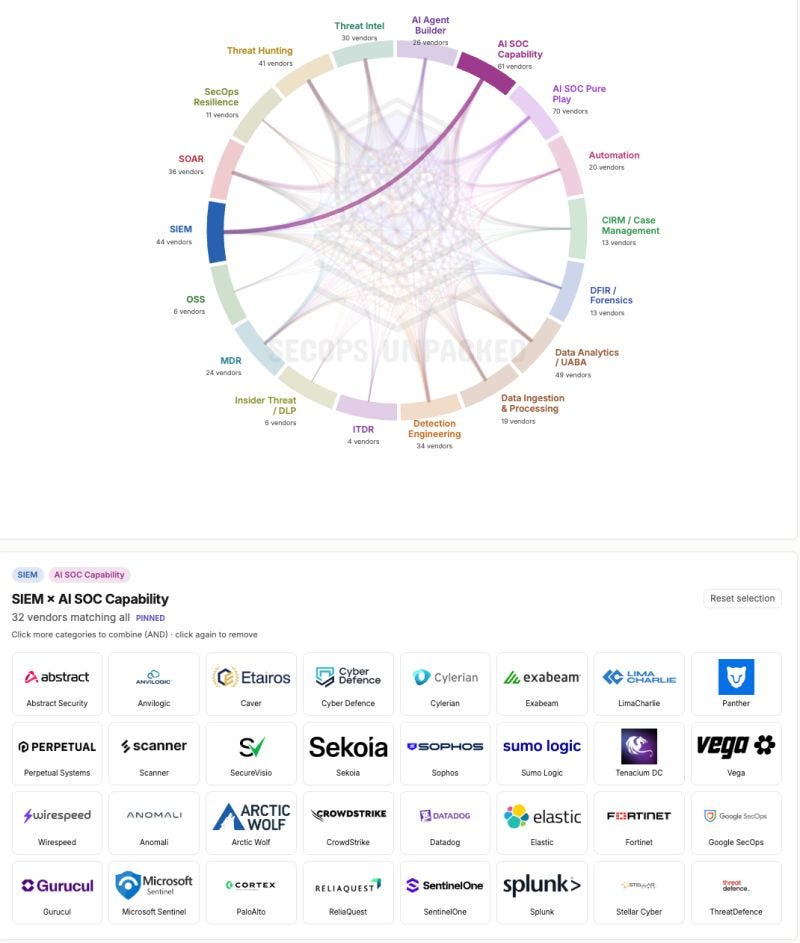
Look at the large players (some might say traditional SIEM). They all have AI SOC now. It became that commoditized.
Some will argue it's not as deep as the pure-play AI SOC vendors.
You're right. It's not.
But what even is AI SOC?
Over the past year I spoke with over 200 practitioners, and AI SOC meant something different to almost every one of them.
In general, I hear: autonomous triage. Close what's noise, escalate what's worth investigating. But triage itself means different things to different people.
Some see basic enrichment. Some expect AI SOC to go deep, even run forensics. Others expect remediation steps staged and ready, so they just approve execution.
I tried creating key components few times, maybe one day they get standardized and we all agree what it should have until than every SIEM can say it has AI SOC.
In my view it should have:
-Data Ingestion and Normalization Engine
-Knowledge Graph (Context is everything)
-Investigation Engine (combo of automations, LLM rules)
-Response (Remediation actions and Feedback Loop)
So yes, every SIEM has AI SOC. How good, how broad, how deep is up to you to decide. On SecOps Unpacked we tagged it, so you can see which vendors expand further and which stay at basic triage.
And guess what. A SIEM with SOAR, AI SOC, and all the other bells and whistles is still called a SIEM. I don't think the name changes anytime soon.
Do you think we should have this checkbox on SecOps unpacked profiles for AI SOC vendors? Does it even matter to you?
Originally posted on LinkedIn on 10 July 2026.
Read the original post and the comments.