

Friday SIEM: The checkbox problem
We track 40 SIEM vendors at SecOps Unpacked. That number surprised me also.
29 are pure-play SIEM with an AI SOC layer. The rest are AI SOC platforms that added SIEM to round out the portfolio.
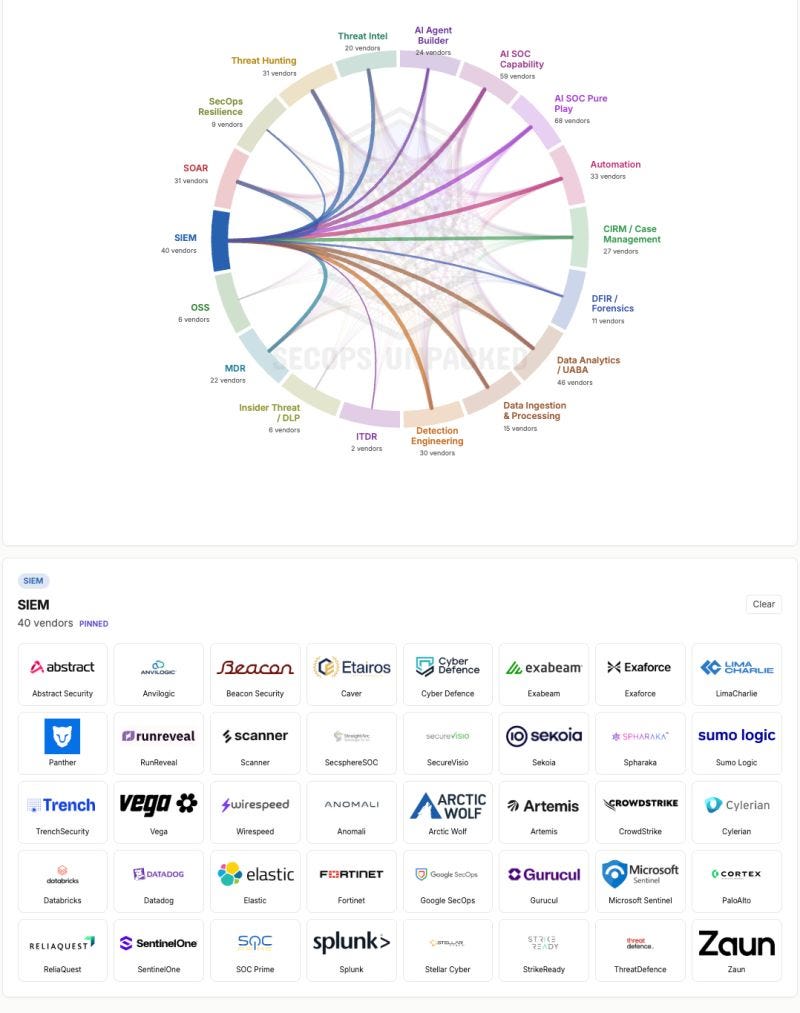
What stands out is how many other categories they touch. Buy a SIEM from one of the larger players and you get SOAR, UEBA, case management, threat intel, vulnerability context, and 15 other things on top of it.
Most of it is checkbox. It exists to survive an RFP, avoid losing a deal, and give the account team an upsell conversation. I do not blame them. I do the same as a practitioner: I check what my SIEM does natively before I go looking for a point solution. 😅
But good enough is doing a lot of work there.
The SIEM wins or loses on detection quality, query performance, and cost at scale. Everything else is table stakes.
What makes this interesting is that when you map all these capabilities across vendors, many are converging on the same footprint. That is exactly what Gartner's ISOC category describes.
So yeah, is there checkbox feature in your SIEM that you really like?
Originally posted on LinkedIn on 19 June 2026.
Read the original post and the comments.