

This week we have the Vibe check Friday SIEM post
Outside of alert triage, AI use cases in SIEM are everywhere in the marketing decks. But what's actually landing in production?
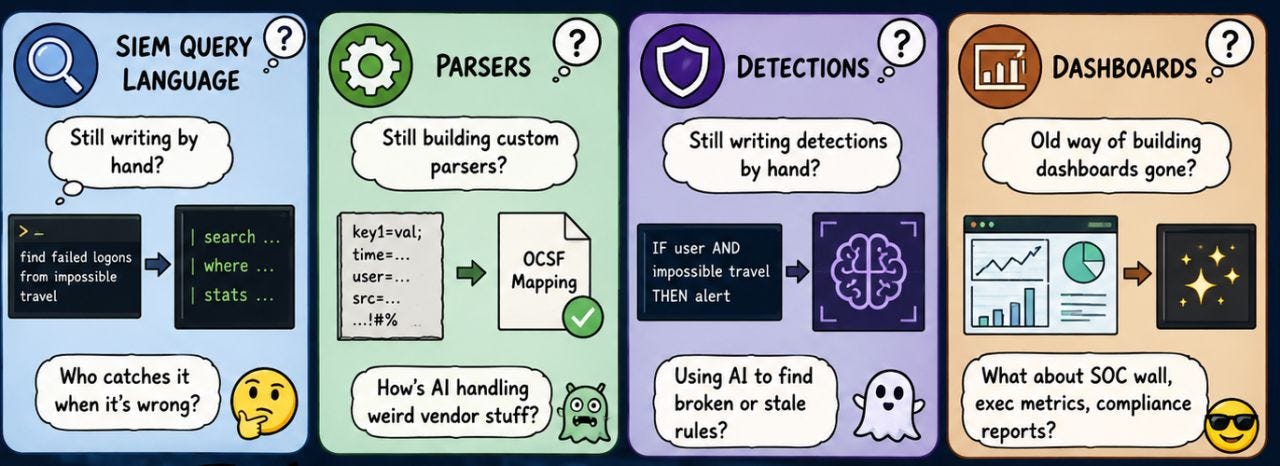
A few questions I'm curious about:
▪️ SIEM Query Language. Is anyone still writing it by hand? Or are your analysts just typing English and letting the LLM generate the query underneath? And when the generated query is wrong, who catches it?
▪️Parsers. Are you still building custom parsers for your messy log sources, or do you trust AI to handle schema translation and OCSF mapping? How is it working on the weird vendor-specific stuff?
▪️Detections. Anyone still constructing detections by hand for the rules that matter? Or is AI writing them now? What about the existing rule estate, are you using AI to find broken or stale rules?
▪️Dashboards. Is the old way of building custom dashboards gone? Are you letting the SIEM generate visuals on the fly during investigations? What about your operational dashboards, SOC wall, exec metrics, compliance reports, are those still hand built?
Curious to here where we stand with these?
Originally posted on LinkedIn on 15 May 2026.
Read the original post and the comments.