

My Friday SIEM post is here, to log or not to log!
Getting Shakespeare vibes, I know. From what I have seen in my career there are 3 approaches.
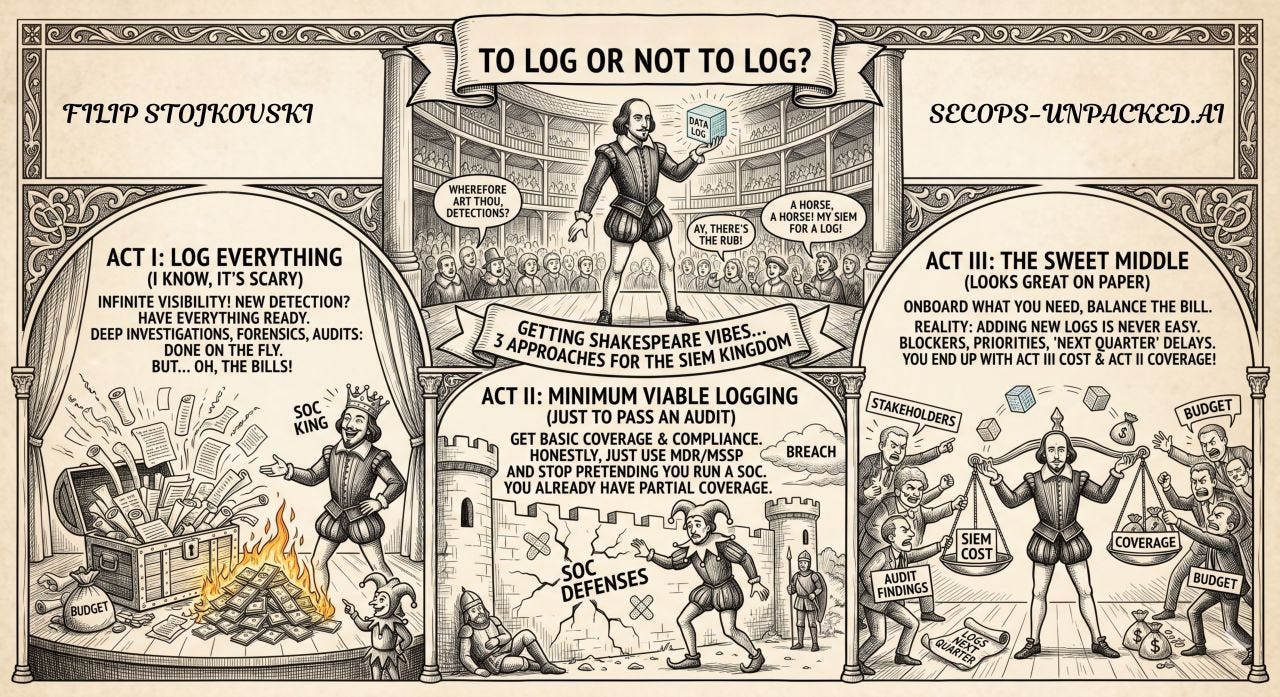
LOG EVERYTHING. I know for some of you this might be scary, you see cash burning instantly, million dollar bills. And yes, depending on the size of the company and the SIEM they use, this might be doable. I have been part of orgs where it was, I loved it. You get a new log source, try to pull as much as possible.
Best part was whenever I needed to create a new detection I would just get everything I needed, no need to go through the log onboarding process again. Additional logs for forensics or deep investigation, I get them right away. Audit comes, we have everything, pass it on the fly.
Then there is the least optimistic way, onboard whatever we need just to have basic coverage and pass an audit or get a cert. Minimal coverage. I think in this case you are better off just using an MDR or MSSP, don't even bother. Anyhow you have partial coverage with them.
And we have the sweet middle, where you onboard just what you need, increase and decrease logs based on usage, you have a nicely balanced bill. In my opinion this one looks good on paper. In reality, adding logs is never easy, simply because of other stakeholders, and you will always have audit findings that need to be prioritized over engineering work. You end up paying close to option 1 and getting close to option 2.
Maybe I'm missing some other approach, let me know.
Originally posted on LinkedIn on 1 May 2026.
Read the original post and the comments.